PRIVACY POLICY
September 2026
FIIG Securities Limited (“FIIG”)
ABN 68 085 661 632 | AFSL 224659
This Privacy Policy is provided by FIIG Securities Limited (FIIG) ABN 68 085 661 632 AFSL 224659 of Level 11, 55 Market Street Sydney NSW 2000.
FIIG Securities Response to Cyber Incident, click here
1. YOUR PRIVACY IS IMPORTANT TO US
We know that how we collect, use, exchange and protect your information is important to you and we value your trust. That’s why protecting your information and advising you about what we do with your information is a vital part of our relationship with you.
Please note that during the course of our relationship with you, we may provide more details about how we handle your information. This could be when you complete an application or receive a terms and conditions document or a Product Disclosure Statement (PDS). When you receive this further information, please consider it carefully and visit our website regularly as we update this policy from time to time.
In addition to the Privacy Act 1988 (Cth), where the European Union General Data Protection Regulation (EU GDPR) or United Kingdom General Data Protection Regulation (UK GDPR) applies to FIIG’s processing of personal information, individuals may also have rights under those laws.
Details of additional rights that may be available to individuals under the EU GDPR or UK GDPR and how we meet them are outlined in Appendix 1. We take privacy seriously and are committed to ensuring the protection of your personal information, regardless of where you are located.
This Privacy Policy does not apply to acts or practices of FIIG that are directly related to employee records of current or former employees to the extent that the employee records exemption under the Privacy Act applies.
2. INFORMATION WE COLLECT
Information we collect from you
We collect your information when you request or use our products or services, transfer money, phone us or visit any of our websites, and when we interact with you to administer any products and services that you have with us.
When you use our website, we may collect information about your location or activity including IP address, telephone number and whether you’ve accessed third party sites. Some of this website information we collect using ‘cookies’.
The information we collect from you may include your identity and contact details, other personal details such as gender and marital status and financial information.
FIIG may also collect information including your date of birth, occupation and employer, tax residency and tax file number, banking details, investments, holdings and transactions, source of funds or source of wealth, and information about companies, trusts, superannuation funds and other entities with which you are associated.
We may collect information about directors, trustees, beneficial owners, controllers and authorised representatives, and information contained in identity documents such as passports, driver licences and Medicare cards. We may also collect information required to meet our anti-money laundering and counter-terrorism financing, sanctions and other legal or regulatory obligations.
FIIG collects information about you when you register on FIIG’s website. This may include registration to attend a FIIG event, download a FIIG publication or register for FIIG’s weekly e-newsletter The WIRE.
Information we collect from other parties
We collect information about you from other parties such as service providers, agents, advisers or brokers, if we have a requirement to do so. We may collect information about you that is publicly available, for example from public registers or social media, or made available by third parties.
Sensitive information
The Privacy Act 1988 also protects your sensitive information, if we need to obtain this type of information, we will ask for your consent prior to collecting your sensitive information (except where otherwise permitted by law).
Electronic identity verification
FIIG may collect and use personal information to verify your identity and meet our legal and regulatory obligations, including under anti-money laundering and counter-terrorism financing laws. With your express consent, information from identification documents you provide may be checked with the relevant document issuer or official record holder via third-party systems for the purpose of confirming your identity. If you do not consent to electronic identity verification, another verification method may be available. However, we may be unable to open or continue an account or provide certain products or services if we cannot verify your identity. Information about how FIIG handles your personal information, including disclosures, retention and destruction, access and correction, and complaints, is set out in sections 4 to 7 of this Privacy Policy.
As part of the onboarding process, FIIG may provide identification document numbers to third-party identity-verification service providers for the limited purpose of verifying your identity. Those service providers do not store that information outside Australia.
Information about the operation and management of the Australian Government’s Document Verification Service is available on the IDMatch website.
Telephone calls
Certain FIIG teams may record all or part of telephone calls with you.
Where calls are recorded, recordings may be used for service quality, training and supervision, investigating complaints or disputes, and meeting legal, regulatory or record-keeping requirements.
FIIG may use artificial intelligence or other automated technologies to transcribe, summarise or analyse recorded telephone calls. These technologies may assist with preparing business records, service quality, training and supervision, investigating complaints or disputes, risk and compliance activities, and meeting legal, regulatory or record-keeping requirements. Call recordings, transcripts and summaries may contain personal information and will be handled in accordance with this Privacy Policy. FIIG personnel remain responsible for reviewing and using outputs produced by these technologies where appropriate.
Call recordings are not intended to replace written confirmation of trade instructions.
Where required, we will notify you that a call is being recorded.
3. HOW DO WE USE YOUR INFORMATION?
We collect, use and exchange your information so that we can:
- establish your identity and assess applications for products and services
- price and design our products and services
- administer our products and services
- administer our customer databases, systems and internal processes
- manage our relationship with you
- manage our risks and help identify and investigate illegal activity, such as fraud
- contact you, for example if we suspect fraud on your account or need to tell you something important
- conduct and improve our businesses and improve the customer experience
- comply with our legal obligations and assist government and law enforcement agencies or regulators
- comply with our international legal and taxation obligations and assist international government entities as required
We may also collect, use and exchange your information in other ways where we are required to do so and where permitted by law.
Gathering and combining data to get insights
Improvements in technology enable organisations, like us, to collect and use information to get a more integrated view of customers and provide better products and services.
We may combine the customer information we have with information available from a wide variety of external sources (for example census or Australian Bureau of Statistics data). This allows us to analyse the data in order to gain useful insights which can be used for any of the purposes mentioned earlier in this section.
In addition, we may provide data insights or related reports to others, for example to help them understand their customers better. These are based on aggregated information and will not contain any information that identifies you.
FIIG may also use or disclose information that has been anonymised or aggregated so that it does not identify you, including to prepare, publish or contribute to reports, research materials, market analysis, statistical insights and other informational content. FIIG will take reasonable steps to ensure that individuals cannot be re-identified from that information.
Artificial intelligence
FIIG may use artificial intelligence, machine learning and other automated technologies to assist our employees and support our business processes.
These technologies may assist with activities such as processing or extracting information from documents, administrative tasks, analysing information, risk and compliance activities, customer service and preparing or reviewing communications or business records. Where these technologies process personal information, that information remains subject to this Privacy Policy and applicable privacy requirements.
FIIG will not use personal information through artificial intelligence or automated technologies in a manner that is inconsistent with the purpose for which the information was collected or with specific restrictions that apply to that information. We may use third-party technology providers in connection with these technologies.
Automated processes
FIIG may use automated systems to apply administrative or eligibility controls. These systems may use personal information such as account information, client status and relevant dates or expiry dates of documents or certificates, including information relevant to a client’s wholesale status. For example, an automated process may restrict access to a product or service where documentation or a status required for access has expired or is no longer current, until the relevant information or status is renewed.
Decisions about whether to onboard a client are made by FIIG personnel.
If FIIG introduces other arrangements involving automated decision-making that are required to be described under applicable privacy law, this Privacy Policy will be updated accordingly.
4. WHO DO WE EXCHANGE YOUR INFORMATION WITH?
We exchange your information with our related entities and certain third parties so that we may adopt an integrated approach to our customers. We may use this information for any of the purposes mentioned in section 3.
FIIG does not sell personal information to third parties.
Third parties
We may exchange your information with third parties where this is permitted by law or for any of the purposes mentioned in section 3. Third parties include:
- our service providers (such as consultants and technology service providers) and those who refer business to us
- co-branding or branding partners (organisations with whom we have agreements to provide products and services under a different brand name)
- those to whom we outsource certain functions, for example, direct marketing, statement production, debt recovery and information technology support
- platform providers, issuers of financial products, other financial institutions, and other bodies
- brokers, agents and advisers, and their service providers, and persons acting on your behalf, for example guardians and persons holding power of attorney
- custodians and sub-custodians, trading counterparties, operators of clearing and settlement facilities and registries
- investment managers and other providers involved in investment or portfolio services
- issuers of financial products, identity verification and screening providers
- other financial institutions, for example so that we can process a claim for mistaken payment
- auditors, insurers and re-insurers
- employers or former employers
- government and law enforcement agencies or regulators
- entities established to assist with anti-money laundering and counter-terrorism financing (AML/CTF) obligations, and/or help identify illegal activities and prevent fraud.
From time to time our third-party service providers/white label partners, for the purposes of meeting regulatory, compliance or legislative requirements, may request that we validate and/or verify your information which you have provided to them. This ensures that your information is correct and they can provide services to you.
When engaging third-party service providers that may handle personal information, FIIG undertakes appropriate due diligence having regard to the nature of the services and information involved. FIIG also seeks to implement contractual, data-handling and security arrangements that are appropriate in the circumstances and to monitor relevant service-provider risks in accordance with its applicable legal and regulatory obligations.
You can request not to have your information shared with third party service providers. However, we may not be able to provide you with our services where we rely on third party service providers to complete certain functions, issue financial products, act on your behalf, or provide custody, settlement and execution facilities for us. If you do not wish your information to be shared, please contact us for further information to discuss your options, using the contact details in section 8.
Marketing Communications
We will use your personal information to send you offers for products and services we believe may be of interest and value to you (including by email, SMS or other means) unless you have previously told us that you do not want to receive marketing offers from us.
If you do not want to receive direct marketing offers from us, you can unsubscribe using the facility included in the communication or let us know via phone or email.
Sending information overseas
From time to time we may send your information overseas, including to our related entities, service providers or other third parties who operate or hold data outside Australia. For example:
- FIIG is a wholly owned subsidiary of Australian Investment Exchange Limited, a wholly owned subsidiary of Nomura Research Institute, Ltd. Your information may be disclosed to NRI group entities and third parties in overseas jurisdictions including: Japan; India; and the Philippines for the purpose of delivering or providing services to you.
- We may also send your information to the services providers who are likely to be located in the USA, UK, Ireland, Germany, European Economic Area, New Zealand, Phillippines, Singapore, Switzerland and South Africa to help us deliver or support the provision of products and services to you e.g. for client screening to meet regulatory obligations.
- Where applicable, we may also send information overseas to complete a particular transaction, such as an International Money Transfer or International Transfer of holdings, or where this is required by laws and regulations of Australia or another country.
Where we send information overseas, we take reasonable steps to assess and address relevant data-handling and security risks, including through appropriate due diligence and contractual or other safeguards where appropriate. Australian privacy law may not apply directly to some overseas recipients.
5. KEEPING YOUR INFORMATION SECURE
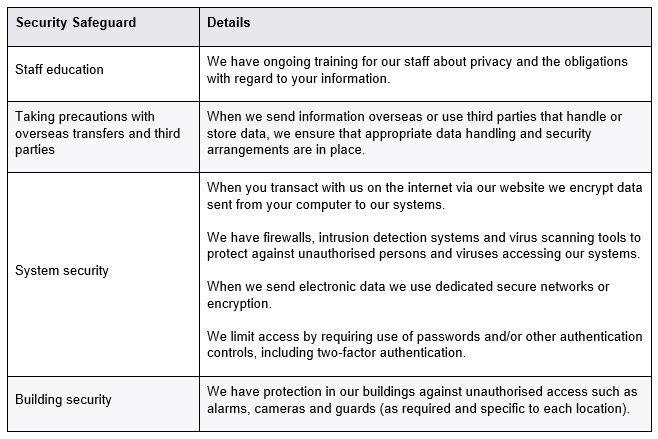
We keep your hard-copy or electronic records on our premises and systems or offsite using trusted third parties. Our security safeguards include:
FIIG retains personal information and related records for as long as reasonably necessary for the purposes for which they were collected or used, and to meet applicable legal, regulatory, contractual, dispute-management and legitimate business requirements. Retention periods may vary according to the nature of the information and the relevant circumstances. When information is no longer required to be retained, FIIG takes reasonable steps to destroy or permanently de-identify it, subject to any lawful basis or requirement for continued retention.
Depending on the circumstances in which you engage with us, including the product or service you apply for, or obtain, from us and whether directly with us or with the support of a third party, all of this Privacy Policy may be relevant to you, in addition to any privacy policy/notice of that third party.
6. ACCESSING, UPDATING AND CORRECTING YOUR INFORMATION
Can I get access to my information?
You can ask for access your basic information (for example what transactions you’ve made) by going online or phoning us using the details provided at the bottom of this policy.
For more substantial information you will need to contact Client Services using the details in section 8.
Is there a fee?
There is no fee for making the initial request, but in some very limited cases there may be an access charge to cover the time we spend locating, compiling and explaining the information you ask for. If there is an access charge, we’ll give you an estimate upfront and confirm that you’d like us to proceed. Generally, the access charge is based on an hourly rate plus any photocopying costs or other out-of-pocket expenses. You’ll need to make the payment before we start, unless you’ve authorised us to debit your account.
How long does it take to gain access to my information?
We try to make your information available within 30 days of your request. Before we give you the information, we’ll need to confirm your identity.
Can you deny or limit my request for access?
In certain circumstances we’re allowed to deny your request, or limit the access we provide. For example we might not provide you access to commercially sensitive information. Whatever the outcome, we’ll write to you explaining our decision.
Updating your basic information
It’s important that we have your correct details such as your current address and telephone number. You can check or update your information by going online or phoning us using the details provided at the bottom of this policy.
Can I correct my information?
You can ask us to correct any inaccurate information we hold or have provided to others by contacting us using the details at the bottom of this policy. If the information that is corrected is information we have provided to others, you can ask us to notify them of the correction. We don’t charge a fee for these requests.
If we’re able to correct your information, we’ll inform you when the process is complete.
What if we disagree that the information should be corrected?
If we disagree with you that information should be corrected, we’ll let you know in writing our reasons. You can ask us to include a statement with the relevant information, indicating your view that the information is inaccurate, misleading, incomplete, irrelevant or out-of-date. We will take reasonable steps to comply with such a request.
7. MAKING A PRIVACY COMPLAINT
We’re here to help
We accept that sometimes we can get things wrong. If you have a concern about your privacy you have a right to make a complaint and we’ll do everything we can to put matters right.
How do I make a complaint?
To lodge a complaint, please get in touch with us using the details set out in section 8. We’ll review your situation and try to resolve it straight away. If you have raised the matter through your point of contact and it has not been resolved to your satisfaction, please contact our Client Services team using the details in in section 8.
How do we handle a complaint?
We acknowledge every complaint we receive and provide our name, a reference number and contact details of the investigating officer. We keep you updated on the progress we’re making towards fixing the problem.
Usually, it takes only a few days to resolve a complaint. However, if we’re unable to provide an Internal Dispute Resolution Response within 30 days we’ll contact you to explain why and discuss a timeframe to resolve the complaint.
External Review
If you’re not satisfied with our handling of your matter, you can refer your complaint to external dispute resolution. We suggest you do this only once you’ve first followed our internal complaint processes set out above.
If you wish to seek external dispute resolution, the Australian Financial Complaints Authority (AFCA) offers a free and independent dispute resolution scheme. You can contact AFCA, GPO Box 3 Melbourne VIC 3001 on:
Phone: 1800 931 678
Email: info@afca.org.au
Online: www.afca.org.au
If your complaint is about the way we handle your personal information, you may also contact the Office of the Australian Information Commissioner on 1300 363 992, online at www.oaic.gov.au or write to the Office of the Australian Information Commissioner, GPO Box 5218, Sydney NSW 2001.
8. HOW TO CONTACT US OR FIND OUT MORE
For privacy related queries, access or correction requests, or complaints, or to request a printed version of this policy please contact us on the details provided below as we aim to resolve your query or complaint at your first point of contact with us.
Client Services
Phone: 1800 01 01 81
Email: clientservices@fiig.com.au
If you have tried to resolve your query through your usual point of contact or Client Services and are not satisfied with the outcome, you can contact:
Complaints Team
Phone: 1800 01 01 81
Email: complaints@fiig.com.au
Post: FIIG Securities Limited, GPO Box 1186, Brisbane QLD 4001
Appendix 1: Additional rights for individuals located in the European Union
The European Union (EU) and United Kingdom (UK) General Data Protection Regulation (GDPR) has harmonised the data privacy laws of each individual EU and UK country, giving more rights to individuals located in the EU or UK and more obligations to organisations holding their personal information. In this Appendix, “personal information” means any information relating to an identified or identifiable natural person (the meaning given to the term “personal data” in the GDPR).
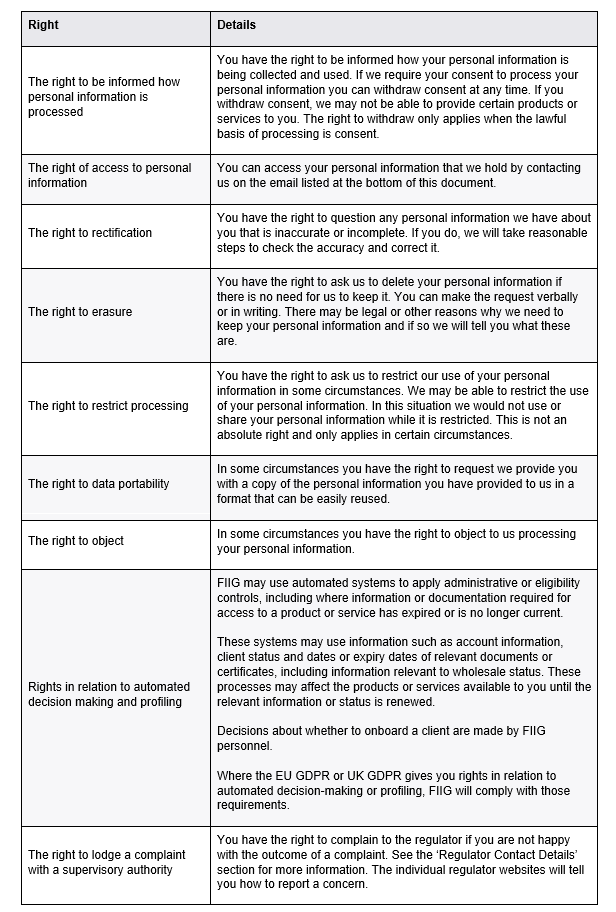
Personal information must be processed in a lawful, fair and transparent manner. As such, if you are located in the EU or UK then GDPR requires us to provide you with more information about how we collect, use, share and store your personal information as well as advising you of your rights as a ‘data subject’.
If the EU GDPR or UK GDPR applies to FIIG’s processing of your personal information and you have an enquiry relating to your rights, please contact us using the details in section 8.
WHAT PERSONAL INFORMATION DO WE COLLECT?
The information about the data we collect in Section 2 of the main Privacy Policy applies.
Special Categories of Personal Information
The GDPR provides additional protection for personal information about your racial or ethnic origin, political opinions, religious or philosophical beliefs, trade union membership, biometric data (for example your fingerprints), or data concerning your health, sex life or sexual orientation. We will only process this type of personal information with your consent or where otherwise lawfully permitted.
How long we keep your personal information
We generally retain your personal information for up to seven years after you stop being a customer. We may retain it for a longer period where reasonably necessary to comply with legal or regulatory obligations, manage or respond to a question, complaint, investigation, claim or dispute, conduct internal research and analytics, prevent or detect fraud or misuse, or meet another lawful business requirement.
9. HOW WE USE YOUR INFORMATION
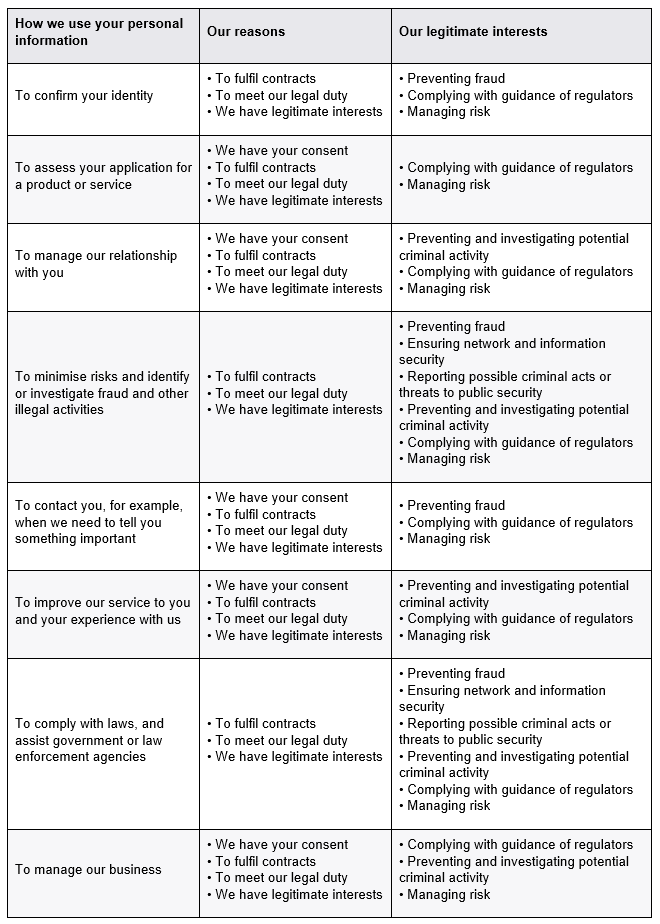
We can only collect and use your personal information if we have a valid lawful reason to do so. For FIIG, these reasons are:
- Contract: We need to process your personal information in order to fulfil a contract you have with us, or because you have asked us to take specific steps before entering into a contract.
- Legal obligations: We need to process your personal information for us to comply with the law (not including contractual obligations).
- Consent: You have given clear consent for us to process your personal information for a specific purpose.
- Legitimate interests: We need to process your personal information for our legitimate interests or the legitimate interests of a third party unless there is a good reason to protect your personal information which overrides these legitimate interests.
Your rights as a data subject
Please note that while any changes you make to your Personal Information will be reflected in active user databases instantly or within a reasonable period of time, we may retain all information you submit for backups, archiving, prevention of fraud and abuse, analytics, satisfaction of legal obligations, or where we otherwise reasonably believe that we have a legitimate reason to do so.
You may decline to share certain personal information with us, in which case we may not be able to provide to you some of the features and functionality of our products and services.
REGULATOR CONTACT DETAILS
The UK data protection authority is:
Information Commissioner’s Office
Wycliffe House
Wilmslow
Cheshire SK9 5AF
UK
Visit: ico.org.uk
For other European jurisdictions please refer to the European Commission website for details of the relevant data protection authorities.
Have questions? Connect with us.
FIIG Securities Limited
GPO Box 1186
Brisbane QLD 4001
Phone: 1800 01 01 81
Email: clientservices@fiig.com.au
Website: fiig.com.au